Shreyas Tamhan
Cybersecurity professional with 12+ years of experience across cyber defense, security operations, incident response, SIEM, EDR/XDR, detection engineering, threat hunting, and security automation. Experienced in security operations leadership, enterprise endpoint security, customer security engagements, security monitoring, and security process improvement through automation and practical cybersecurity solutions.
SentinelOne Automation Platform
Automation for Security Operations
Python-based automation platform leveraging SentinelOne APIs to streamline repetitive security operations tasks, improve analyst productivity, and enhance operational efficiency.
Open Project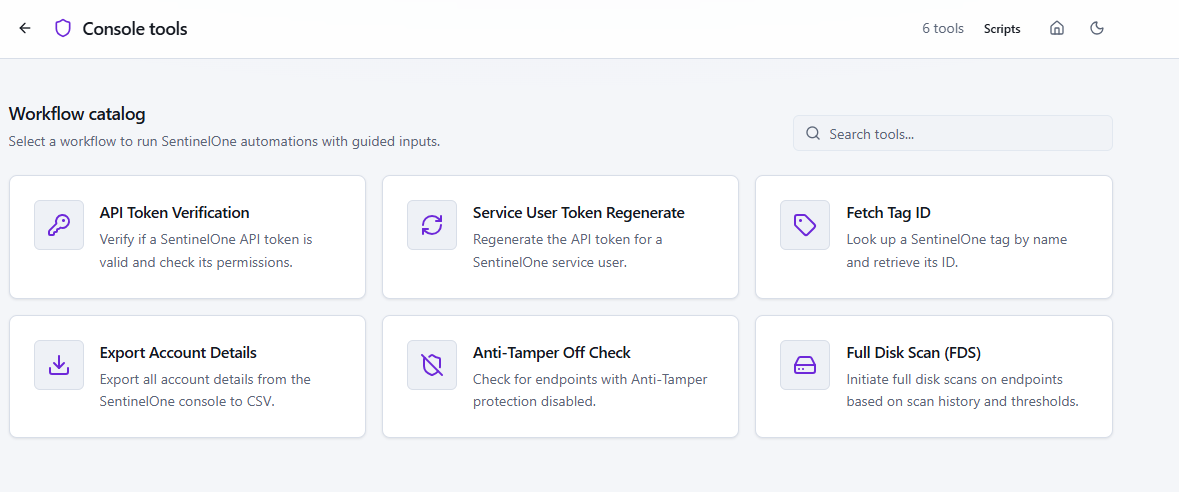
Areas of Practice
Security Operations
SOC processes, monitoring and incident handling.
Threat Hunting
Proactive investigation and threat discovery.
Security Automation
Reducing manual effort through automation.
Detection Engineering
Building actionable security detections.
Incident Response
Investigation and containment of threats.
Security Engineering
Security tooling, automation, detection capabilities, and operational security improvements.